
Advisory / retained / limited capacity
Advisory
I advise a small number of companies on security architecture through a dedicated monthly cadence. You bring the architecture, the roadmap, and whatever is on your mind. I tell you what I think.
Why this lens
Most security measures reduce risk. A few remove the attack surface altogether. The 76 analyses on this site argue that the difference between the two is measurable.
Of those, 76 are scored against the four invariants. The best three together would have prevented or significantly mitigated 47. That is the lens I bring to a conversation.
Who is advising
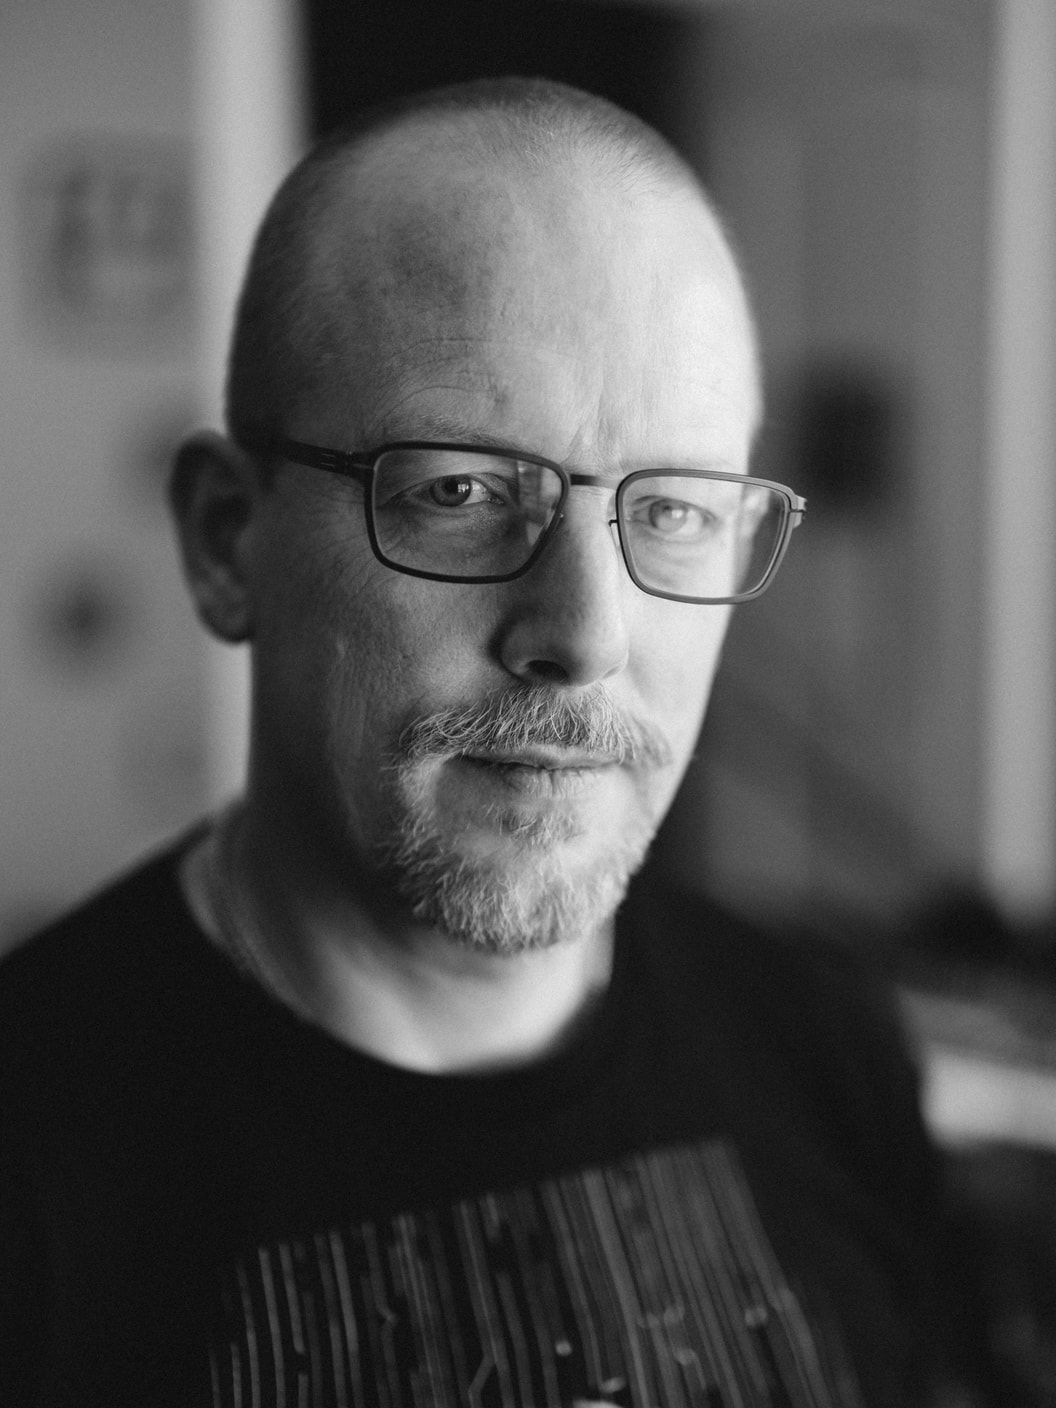
In 1999, Niels Provos drove to Canada to strip the encumbered cryptography out of OpenSSH, because United States export law would not let him do the work at home. OpenBSD could then release the code worldwide. He and David Mazières published bcrypt the same year; it still hashes passwords at companies founded two decades later. Honeyd and libevent followed.
Google hired him into its security organization in 2003, where he defended the company against denial-of-service attacks and helped start Safe Browsing in 2006. He ran the team for seven years, which is why Chrome, Firefox and Safari warn you before you open a malicious page. As a Distinguished Engineer, he spoke at Google I/O on how Google secures its infrastructure. In 2018, Stripe made him Head of Security; from 2022 to 2024, he led security efficacy at Lacework.
Anthropic’s Mythos agent found a signed-integer comparison in OpenBSD’s TCP SACK code that could panic the kernel. It had survived twenty-seven years of review. Provos wrote it in 1998, while finishing his doctorate at Michigan, and confirmed the mistake was his. He reproduced the result independently with IronCurtain, his open-source agent runtime, on models anyone can rent, for tens to low hundreds of dollars an audit. Patching faster will not keep up with that. The controls that put a whole class of bug out of reach will.
Security Blueprints puts that argument on the record. 76 breaches taken down to root cause, scored against structural controls, answer a question the industry mostly guesses at: which controls prevent breaches, and by how much. He wrote PlanAI to run the analysis and is building CISO Challenge, a simulation of the funding decisions that produce breaches. Running security engineering teams for fifteen years taught him the rest. The hardest part of an invariant is rarely technical; it is getting an organization to adopt one.
How it works
- Cadence
- A dedicated monthly cadence; typically 1 to 3 strategy sessions depending on the engagement and email access for questions between calls.
- Scope
- High-leverage security architecture decisions in front of you. Invariants are where we start; the conversation goes wherever the friction is.
- Form
- Direct advisory. You bring the architecture, roadmap, and design trade-offs; I give you candid, independent evaluation.
- Capacity
- Retained at a defined monthly allocation. I work with only a handful of clients at a time so every conversation gets real focus.
What it is not
- Not an audit.
- Not a compliance exercise.
- Not a penetration test.
- Not an extra pair of hands.
- No report at the end.
You get grounded, deeply experienced technical feedback in real time. If your team needs formal deliverables or written reports, this is the wrong engagement.
The method, in public
- The four invariantsWhat each one is, and the breaches it would have stopped.
- Invariant effectiveness leaderboardHow the scoring works, and what it shows across 76 analyses.
- Three security invariants: a CISO challengeThe argument, aimed at the people who have to fund it.
- JADEPUFFER Agentic Ransomware Campaign via Langflow CVE-2025-3248 (2026)A representative analysis, taken down to root cause.
Start a conversation
Six fields. The message is the one that matters; the more specific you are, the better a first conversation will be. You will get an email to confirm the address, then a reply from me within a few days.